Vault Config Operator

Vault Config Operator with Kanvas

Collaborative and visual infrastructure as design for Vault Config Operator

Features

  • Automates Vault configuration management
  • Simplifies secret management
  • Integrates with Kubernetes resources

Overview

Vault Config Operator is a Kubernetes operator for managing HashiCorp Vault configurations.

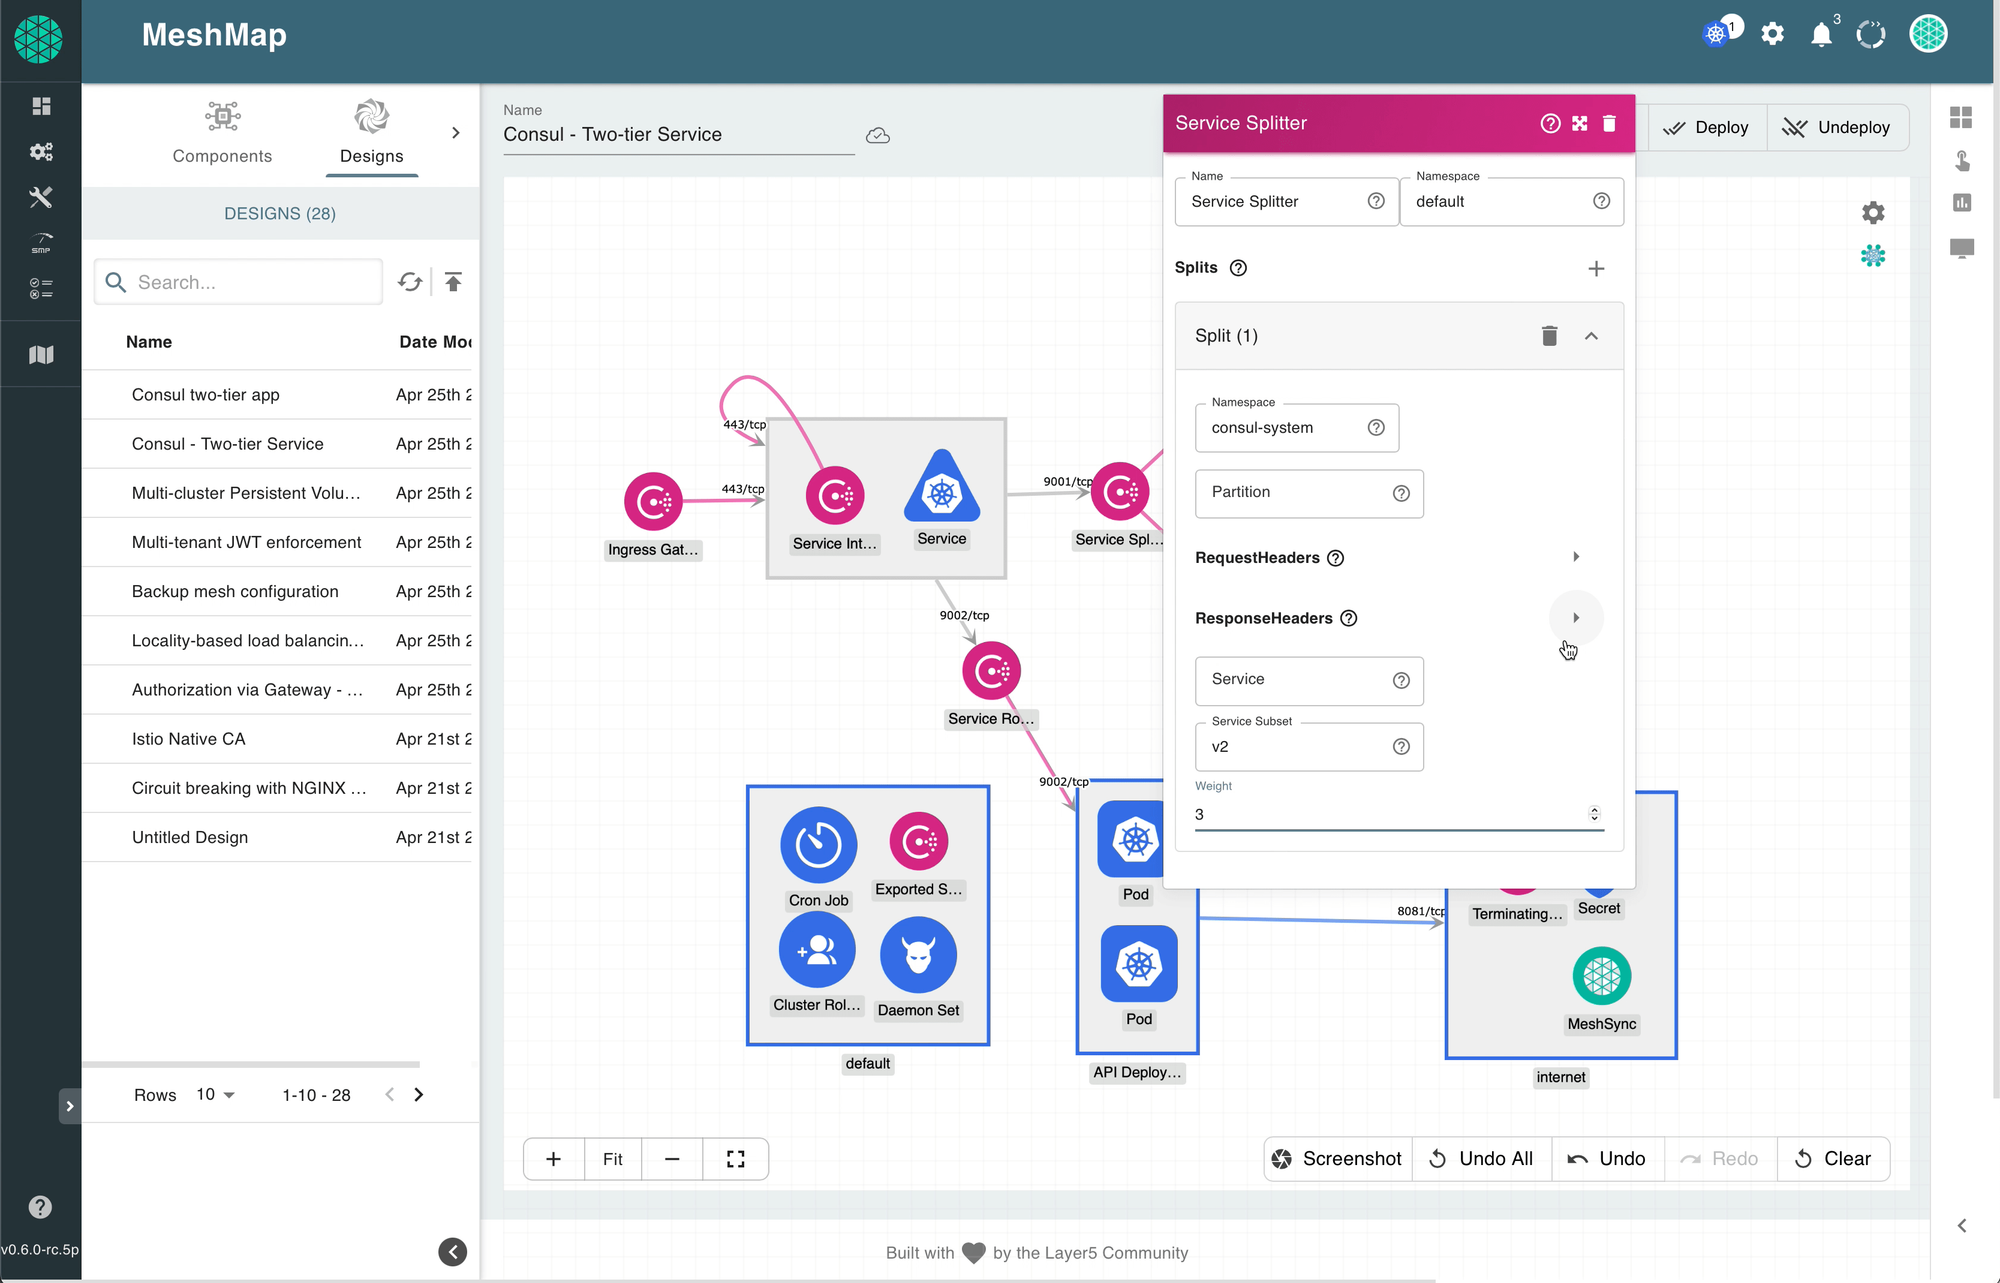
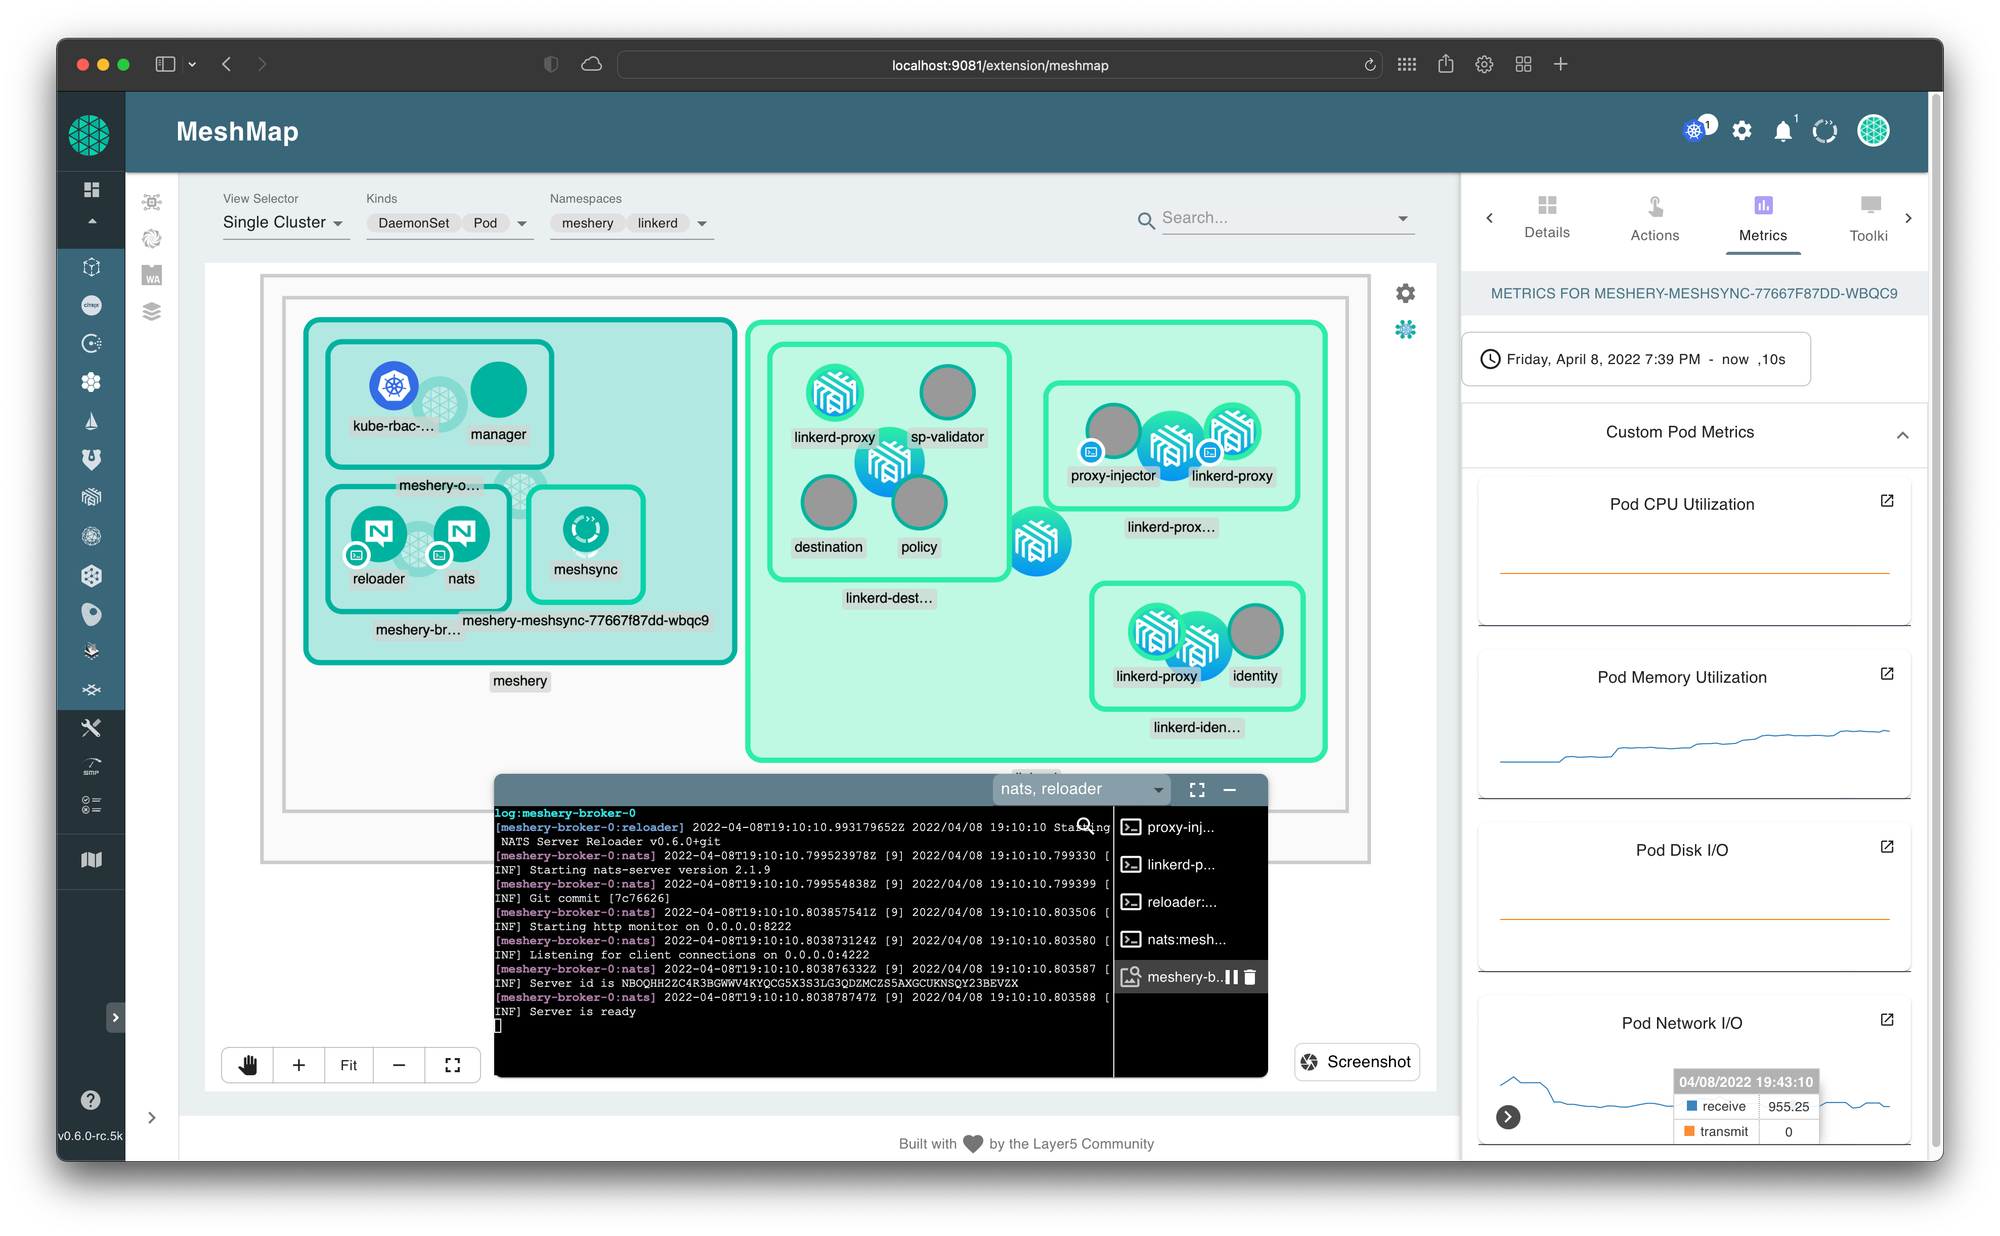
Collaboratively and visually diagram your cloud native infrastructure with GitOps-style pipeline integration. Design, test, and manage configuration your Kubernetes-based, containerized applications as a visual topology.

Looking for best practice cloud native design and deployment best practices? Choose from thousands of pre-built components in Kanvas. Choose from hundreds of ready-made design patterns by importing templates from Meshery Catalog or use our low code designer, Kanvas, to create and deploy your own cloud native infrastructure designs.

See Documentation

Vault Config Operator Components (50)

auth-engine-mountauth-engine-mount

auth engine mount

database-secret-engine-configdatabase-secret-engine-config

database secret engine config

database-secret-engine-roledatabase-secret-engine-role

database secret engine role

database-secret-engine-static-roledatabase-secret-engine-static-role

database secret engine static role

git-hub-secret-engine-configgit-hub-secret-engine-config

git hub secret engine config

git-hub-secret-engine-rolegit-hub-secret-engine-role

git hub secret engine role

jwtoidc-auth-engine-configjwtoidc-auth-engine-config

jwtoidc auth engine config

jwtoidc-auth-engine-rolejwtoidc-auth-engine-role

jwtoidc auth engine role

kubernetes-auth-engine-configkubernetes-auth-engine-config

kubernetes auth engine config

kubernetes-auth-engine-rolekubernetes-auth-engine-role

kubernetes auth engine role

kubernetes-secret-engine-configkubernetes-secret-engine-config

kubernetes secret engine config

kubernetes-secret-engine-rolekubernetes-secret-engine-role

kubernetes secret engine role

ldap-auth-engine-configldap-auth-engine-config

ldap auth engine config

ldap-auth-engine-groupldap-auth-engine-group

ldap auth engine group

password-policypassword-policy

password policy

pki-secret-engine-configpki-secret-engine-config

pki secret engine config

pki-secret-engine-rolepki-secret-engine-role

pki secret engine role

quay-secret-engine-configquay-secret-engine-config

quay secret engine config

quay-secret-engine-rolequay-secret-engine-role

quay secret engine role

quay-secret-engine-static-rolequay-secret-engine-static-role

quay secret engine static role

rabbit-mq-secret-engine-configrabbit-mq-secret-engine-config

rabbit mq secret engine config

rabbit-mq-secret-engine-rolerabbit-mq-secret-engine-role

rabbit mq secret engine role

random-secretrandom-secret

random secret

secret-engine-mountsecret-engine-mount

secret engine mount

vault-secretvault-secret

vault secret

policypolicy

policy

group-aliasgroup-alias

group alias

groupgroup

group

azure-auth-engine-configazure-auth-engine-config

azure auth engine config

azure-auth-engine-roleazure-auth-engine-role

azure auth engine role

azure-secret-engine-configazure-secret-engine-config

azure secret engine config

gcp-auth-engine-configgcp-auth-engine-config

gcp auth engine config

gcp-auth-engine-rolegcp-auth-engine-role

gcp auth engine role

gcp-auth-engine-rolegcp-auth-engine-role

gcp auth engine role

azure-secret-engine-roleazure-secret-engine-role

azure secret engine role

cert-auth-engine-configcert-auth-engine-config

cert auth engine config

cert-auth-engine-rolecert-auth-engine-role

cert auth engine role

cert-auth-engine-rolecert-auth-engine-role

cert auth engine role

audit-request-headeraudit-request-header

audit request header

auditaudit

audit

entityentity

entity

entity-aliasentity-alias

entity alias

identity-oidc-assignmentidentity-oidc-assignment

identity oidc assignment

identity-oidc-clientidentity-oidc-client

identity oidc client

identity-oidc-provideridentity-oidc-provider

identity oidc provider

identity-oidc-scopeidentity-oidc-scope

identity oidc scope

identity-token-configidentity-token-config

identity token config

identity-token-keyidentity-token-key

identity token key

identity-token-roleidentity-token-role

identity token role

identity-token-roleidentity-token-role

identity token role

Kubernetes Orchestration and Diagramming software

Orchestrate and design Kubernetes architecture diagrams easily with predefined templates and symbols designed for professionals.

  • Extensive library of integrations
  • Infrastructure orchestration
  • Multi-player editing
  • Ready-to-use templates
  • Visual drag & drop
  • Operate with No Code

How it Works

See It in Action

Better together - Vault Config Operator with Meshery

Manages Vault configurations

Streamlined Vault configuration management within Kubernetes

Slide 1

Related Integrations

390+ Built-In Integrations

Support for your Cloud Native Infrastructure and Apps

All (382)

Provisioning (68)

App Definition and Development (82)

Platform (6)

Cloud Native Network (42)

Database (19)

    Layer5 is the steward of Meshery and creator of Kanvas, the collaborative canvas for cloud-native infrastructure. We bridge the gap between design and operation, allowing engineers to create, configure, and deploy orchestratable diagrams in real time. Whether managing Kubernetes or multi-cloud environments, Layer5 provides the tooling needed to oversee modern infrastructure with confidence.