

Istio Ingress Gateway in Kubernetes
Predominantly, Kubernetes has used an Ingress controller to handle the traffic that enters the cluster from the outside. Istio has replaced all the familiar Ingress resource with new Gateway and VirtualServices resources. They work in sync to route all the traffic into the mesh. Inside the mesh there is no requirement for Gateways since the services can access each other by a cluster local service name.
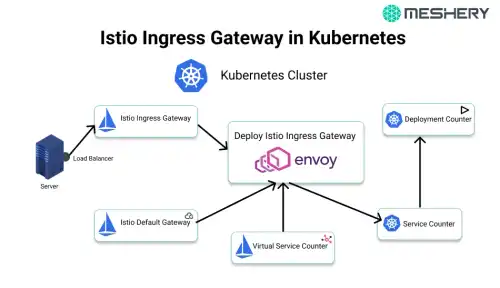
Let’s understand the working with a representation

- Firstly A request is made by a client on a specific port
- Then a load balancer on this port listens and forwards the request to one of the workers in theh cluster on same or a new port
- Inside the cluster the request is routed to the Istio Ingress Gateway which is listened on the port of the load balancer
- The Service forwards the requestto an Istio Ingress Gateway Pod which is managed by a deployment
- The Ingress Gateway Pod is configured by a Gateway and a VirtualService.
- The Gateway configures all the ports, protocol, and certificates.
- The Virtual Service configures all the routing information to find the correct Servicein it.
- The Istio Ingress Gateway Pod routes the request to the application Service.
- And lastly, the application Service routes the request to an application Pod which is managed by a deployment.
Ingress Gateway Service
The Ingress Gateway Service must listen to all the ports to be able to forward the traffic to the Ingress Gateway pods. Here we will be using routing to bring all the port numbers back to their initial state.
Note that a Kubernetes Service is not a real service, but, since we are using type: "NodePort", all the request will be handled by the kube-proxy provided by Kubernetes and forwarded to a node with a current running pod. Once on the node, an IP-tables is configured a request will be forwarded to the appropriate pod.
12# From the istio-ingressgateway service3 ports:4 - name: http25 nodePort: 300006 port: 807 protocol: TCP8 - name: https9 nodePort: 3044310 port: 44311 protocol: TCP12 - name: mysql13 nodePort: 3030614 port: 330615 protocol: TCP
If we inspect the service, we will see that it defines more ports than we have describe above. So these ports will be used for all the internal Istio communication.
Ingress Gateway Deployment
It's a wrapper around the Envoy proxy and it is configured as the sidecars used inside the service mesh. When a Gateway or VirtualService gets changed, they are detected by the Istio Pilot controller and converts this information to an Envoy configuration and sends it to all the proxies, including the Envoy inside the IngressGateway.
Since container ports are not supposed to be declared in Kubernetes pods, we don't have to declare the ports in the Ingress Gateway Deployment. If we look inside the deployment we can see that there are a number of ports that are already declared anyway. We have to take care about the Ingress Gateway Deployment in SSL certificates. To access the certificates inside the Gateway resources, make sure that we have mounted all the required certificates properly.
12# Example represents volume mounts3volumeMounts:4- mountPath: /etc/istio/ingressgateway-certs5 name: ingressgateway-certs6 readOnly: true7- mountPath: /etc/istio/ingressgateway-ca-certs8 name: ingressgateway-ca-certs9 readOnly: true1011# Example represents volumes12volumes:13- name: ingressgateway-certs14 secret:15 defaultMode: 42016 optional: true17 secretName: istio-ingressgateway-certs18- name: ingressgateway-ca-certs19 secret:20 defaultMode: 42021 optional: true22 secretName: istio-ingressgateway-ca-certs
The Gateway
The Gateway resources are used to configure the ports for Envoy and also support for the Kubernetes Ingress. Since all the three ports are exposed with the servies, we need these ports to be handled by the Envoy. It can be handled by declaring one or more Gateways.
12apiVersion: networking.istio.io/v1alpha33kind: Gateway4metadata:5 name: default-gateway6 namespace: istio-system7spec:8 selector:9 istio: ingressgateway10 servers:1112 - hosts:13 - '*'14 port:15 name: http16 number: 8017 protocol: HTTP1819 - hosts:20 - '*'21 port:22 name: https23 number: 44324 protocol: HTTPS25 tls:26 mode: SIMPLE27 privateKey: /etc/istio/ingressgateway-certs/tls.key28 serverCertificate: /etc/istio/ingressgateway-certs/tls.crt2930 - hosts: # For all the TCP routing this fields will be ignored, but it will be matched31 - '*' # with the VirtualService, We use * since it will match anything.32 port:33 name: mysql34 number: 330635 protocol: TCP
VirtualService
The last interesting resource we have is the VirtualService, it used in concert with the Gateway to configure Envoy.
A general configuration for an HTTP(s) service
12apiVersion: networking.istio.io/v1alpha33kind: VirtualService4metadata:5 name: counter6spec:7 gateways:8 - default-gateway.istio-system.svc.cluster.local9 hosts:10 - counter.lab.example.com11 http:12 - match:13 - uri:14 prefix: /15 route:16 - destination:17 host: counter18 port:19 number: 80
Application Service and Deployment
The request have now reached the application service and deployment. These are normal Kubernetes resources.
Extras:
Debugging Istio Gateway
First we will use istioctl to check the configuration status of Istio Ingress Gateway:
12# istioctl proxy-status istio-ingressgateway-5586f47659-r64lb.istio-system3Clusters Match4Listeners Match5Routes Match
If anything does not get synced with it, try restarting the ingress gateway pod once - it may be possible that it somehow an update got missed. If RDS looked good, we can check access logs of it.
12#kubectl get configmap istio -n istio-system -o yaml | grep "accessLogFile: "3disable access log.\naccessLogFile: \"/dev/stdout\"\n\n# If accessLogEncoding
Once all the access logs are enabled, we can try torequest a few more times and check the logs on the Ingress Gateway:
12# kubectl logs -n istio-system istio-ingressgateway-5586f47659-r64lb | grep -v deprecated


Layer5 is the steward of Meshery and creator of Kanvas, the collaborative canvas for cloud-native infrastructure. We bridge the gap between design and operation, allowing engineers to create, configure, and deploy orchestratable diagrams in real time. Whether managing Kubernetes or multi-cloud environments, Layer5 provides the tooling needed to oversee modern infrastructure with confidence.